
Web & API penetration testing
OWASP Top 10 and business-logic testing of your apps and APIs.
Most breaches start with something ordinary — a forgotten admin page, a leaked password, an outdated plugin. I test your web apps, APIs and servers the way an attacker would, then help you fix what I find.
Reports are written for both developers and owners: what the risk is, how it can be exploited and exactly how to close it.
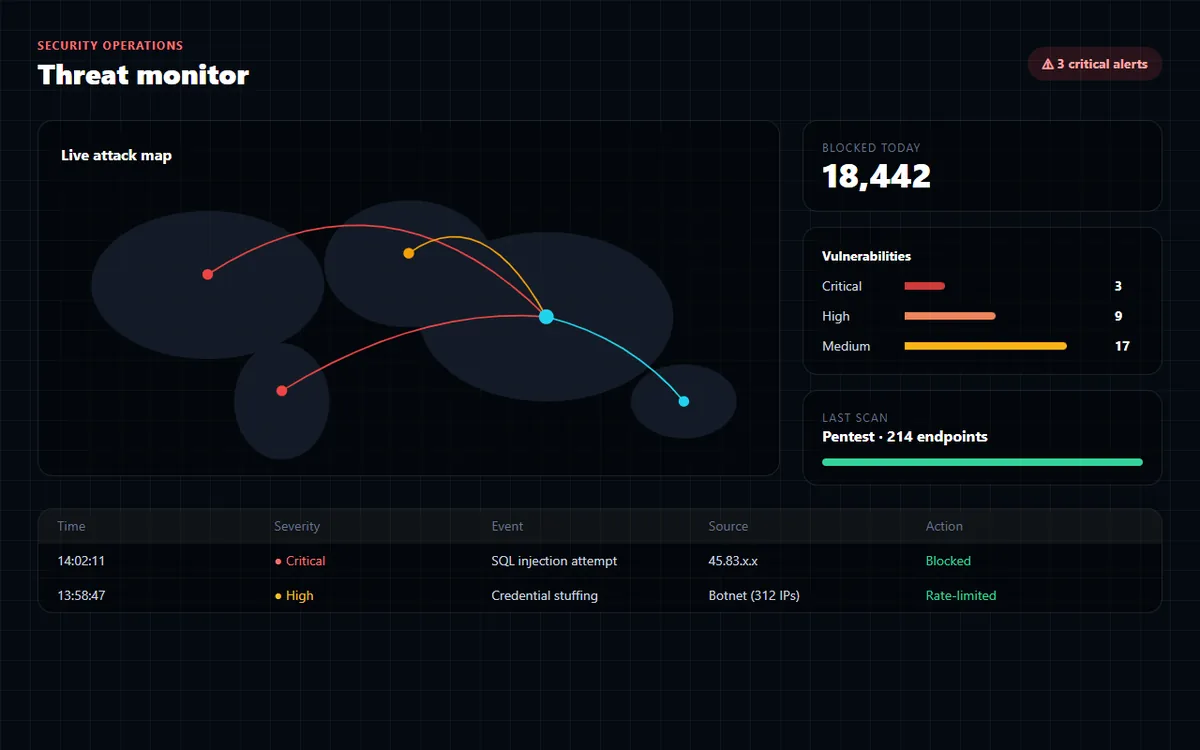
OWASP Top 10 and business-logic testing of your apps and APIs.
Source code checked for injection, auth and data-exposure flaws.
Firewalls, headers, permissions, patching and secrets management.
Infected sites cleaned, backdoors removed and the entry point closed.
Contain, investigate and recover after a breach.
Prompt-injection and data-leakage testing for LLM apps.
Signed scope listing exactly what may be tested and when.
Automated scanning plus manual testing of real attack paths.
Findings with severity, proof and step-by-step fixes.
Help with fixes, then a re-test to confirm they hold.
Testing is scoped and scheduled with you, avoids destructive actions and can run against a staging copy for risky checks.
Yes. I only test systems you own or are authorised to test, under a signed scope.
A report with each finding, its severity, proof and step-by-step fix — plus a re-test after fixes.
Yes — remove malware and backdoors, find how attackers got in, close the hole and harden the site.
Send a short message on WhatsApp — a rough idea is enough. You will get questions, a plan and a quote.